Compliance in Healthcare
Corporate Compliance

When Compliance Meets Forensics

Why Every Healthcare Organization Needs an Internal Investigator 

Written By: Dr. Stacey R. Atkins, PhD, MSW, LSW, CPC, CIGE 

Abstract 

In today’s complex healthcare environment, compliance alone is insufficient to detect and prevent misconduct, fraud, and abuse. Rising regulatory scrutiny, financial pressures, and technological complexity demand a proactive approach that blends compliance oversight with forensic auditing. This article introduces the concept of forensic auditing in healthcare, explains how internal investigators identify and mitigate internal risks before they escalate, and provides a real-world scenario that demonstrates the practical application of forensic principles. As the first in a three-part series aligned with the Certified Internal Forensic Healthcare Auditor (CIFHA) curriculum offered by the American Institute of healthcare Compliance (AIHC), this article establishes why healthcare organizations need internal forensic investigators to ensure accountability, compliance, and integrity across systems and staff.

Introduction

Healthcare organizations operate within one of the most highly regulated industries in the United States. Federal oversight through the Centers for Medicare and Medicaid Services (CMS), the Department of Justice (DOJ), and the Office of Inspector General (OIG) combined with state and accreditation requirements create a multifaceted compliance landscape. As regulatory expectations evolve, organizations must go beyond compliance checklists and adopt investigative capabilities that actively detect and mitigate risk. According to the Office of Inspector General’s 2023 guidance, healthcare compliance programs should include mechanisms for internal investigation and response to suspected violations to ensure early detection and self-disclosure opportunities.

Traditional compliance programs rely on audits and monitoring to identify irregularities and though these methods are proven; these processes are often periodic and limited in scope. Forensic auditing, on the other hand, integrates data analytics, investigative interviewing, and financial tracing to uncover intentional misconduct, hidden patterns, or emerging risks. When integrated within a compliance program, internal forensic investigators bridge the gap between prevention and enforcement.

Defining Forensic Auditing in Healthcare

Forensic auditing combines accounting, auditing, and investigative techniques to identify financial or operational irregularities that could indicate fraud, waste, or abuse. It differs from routine auditing because it assumes concealment, deception, and intent. Forensic auditing emphasizes verification, evidence preservation, and analytical reconstruction of transactions to determine whether misrepresentation occurred. According to the Association of Certified Fraud Examiners’ 2024 Report to the Nations, healthcare fraud remains one of the costliest forms of occupational abuse, with average losses exceeding $100,000 per incident in the provider sector.

Healthcare organizations are especially vulnerable because of the complexity of coding and billing systems, fragmented data environments, and third-party relationships. Forensic auditing in healthcare may involve reviewing claims data, vendor payments, procurement contracts, or physician compensation models. According to CMS program integrity data (2023), more than $60 billion in estimated improper payments were made across federal healthcare programs last year—highlighting the ongoing need for internal vigilance.

Roles, Skills, and Governance of an Internal Forensic Investigator

An internal forensic investigator provides a specialized function within the compliance ecosystem. This professional must possess a blend of analytical, legal, and ethical expertise. Recommended competencies include knowledge of healthcare reimbursement models, coding accuracy, and claims analysis; strong investigative skills such as interviewing, documentation review, and evidence preservation; and familiarity with relevant statutes including the False Claims Act, Anti-Kickback Statute, and HIPAA Privacy Rule.

The investigator’s independence is critical. According to the DOJ’s 2020 Evaluation of Corporate Compliance Programs, the credibility of internal investigations depends on independence, competence, and appropriate resources. Investigators should report directly to the Compliance Officer, Board Audit Committee, or General Counsel to avoid conflicts of interest. Collaboration with IT, Human Resources, and Finance is often necessary for effective data gathering and root-cause analysis.

Training and certification enhance credibility. Many investigators pursue credentials such as Certified Fraud Examiner (CFE), Certified in Financial Forensics (CFF), or Certified Professional Compliance Officer (CPCO). The CIFHA curriculum integrates these skill sets by combining investigative methods with forensic analytics and compliance oversight principles, preparing professionals to handle internal inquiries ethically and effectively.

A Realistic Scenario: The Case of EchoHealth Radiology Network

EchoHealth Radiology Network, a midsize radiology provider, noticed a rise in payer denials and outlier utilization trends within its Magnetic Resonance Imaging (MRI) service line. Routine audits did not reveal significant errors, but a compliance analyst flagged a spike in modifier use for certain spinal studies. The internal investigator initiated a forensic review and uncovered that one radiology group had systematically upcoded imaging services at the direction of a billing manager. Interviews revealed that coders were encouraged to “maximize revenue” by adding modifiers without sufficient documentation.

  • The investigator traced the pattern across six facilities, identified more than $1.2 million in questionable claims, and confirmed documentation gaps.
  • Because the issue was identified internally, EchoHealth voluntarily disclosed the overpayments, retrained coding staff, and implemented a pre-billing review process. The early forensic response protected the organization from potential False Claims Act liability, demonstrated good-faith remediation, and reinforced a culture of compliance and accountability.

Key Benefits and Return on Investment

According to the Government Accountability Office (GAO, 2023), proactive detection and response programs can reduce fraud-related losses by as much as 40 percent. The presence of an internal investigator also promotes a culture of transparency and reinforces the ethical tone of leadership. Internal forensic capacity delivers benefits such as early risk identification, reduced penalties through self-disclosure, improved internal controls, and measurable cost avoidance. Organizations that invest in forensic auditing capability often discover that the savings from avoided regulatory penalties and recovered funds exceed the cost of the program itself.

  • From a compliance culture standpoint, the visibility of an internal investigator acts as a deterrent. 

Employees are more likely to report concerns through proper channels when they see issues being addressed promptly and professionally. This aligns with the OIG’s emphasis on maintaining effective lines of communication and timely corrective action in healthcare compliance programs (OIG, 2023).

Challenges, Limitations, and Mitigations

Despite its value, integrating forensic auditing within compliance presents challenges. Resource limitations are common, particularly for smaller providers. Legal considerations such as maintaining privilege and confidentiality require coordination with counsel. Data analytics and automation can introduce false positives that distract investigators from genuine issues. To mitigate these challenges, organizations can start with pilot programs, outsource complex investigations as needed, and establish clear investigation protocols aligned with OIG and DOJ standards.

Another challenge involves maintaining staff trust. Employees may perceive investigations as punitive rather than corrective. Compliance leaders can address this by communicating the purpose of forensic reviews as a means of protecting both the organization and its workforce. Transparency, education, and post‑investigation feedback sessions can reduce anxiety and improve cooperation.

Alignment with CIFHA Goals

Certified Internal Forensic Auditor

This article—the first in a three-part series—introduces an essential component of the CIFHA curriculum: the intersection between compliance and forensics, embodied in the role of the internal investigator. The next two articles in this series will continue to build upon this foundation:

  • Article 2: “10 Common Mistakes in Internal Investigations—And How to Avoid Them” will draw directly from the CIFHA course section on Accepting the Investigation. It will offer practical insights into how investigators can recognize and avoid common sources of bias, procedural missteps, and compliance pitfalls that compromise investigative integrity.
  • Article 3: “From Findings to Action: Writing an Objective, Defensible Investigative Report” will focus on the analytical and reporting phase—how to synthesize data, present factual findings, and communicate results effectively and ethically. It will demonstrate how the course equips participants to transform raw information into defensible, actionable reports that withstand regulatory and legal scrutiny.

Together, these articles trace the natural progression of the investigative process—from recognizing the need for internal forensics, to conducting unbiased inquiries, to articulating findings that drive organizational accountability and improvement.

Conclusion

Healthcare organizations that embed forensic auditing within compliance are better positioned to detect misconduct, preserve integrity, and demonstrate proactive risk management. According to the DOJ and OIG, organizations that identify and correct issues internally are viewed more favorably in enforcement actions. Internal investigators serve as both a safeguard and a strategic asset—protecting financial integrity while promoting an ethical culture. As healthcare continues to evolve, forensic auditing will remain a cornerstone of mature compliance programs that prioritize transparency, accountability, and continuous improvement.

About the Author - Dr. Stacey R. Atkins, PhD, MSW, LMSW, CPC, CIGE

Dr. Atkins is a Compliance Specialist working as a team member in the Education Department of the American Institute of Healthcare Compliance. Her career spans leadership roles with the Office of the State Inspector General, Department of Behavioral Health and Developmental Services, and HRSA, among others.

References

  • Office of Inspector General (OIG). (2023). Compliance Program Guidance for Hospitals.
  • U.S. Department of Justice (DOJ). (2020). Evaluation of Corporate Compliance Programs.
  • Association of Certified Fraud Examiners (ACFE). (2024). Report to the Nations on Occupational Fraud and Abuse.
  • Centers for Medicare & Medicaid Services (CMS). (2023). Improper Payments Data.
  • Government Accountability Office (GAO). (2023). Fraud Risk Management Framework.
  • Health Care Compliance Association (HCCA). (2024). Best Practices in Internal Investigations.
  • Office of Inspector General (OIG). (2023). General Compliance Program Guidance.
  • U.S. Department of Health and Human Services (HHS). (2024). Health Care Fraud and Abuse Control Program Annual Report.
  • Compliance Week. (2023). The Rising Role of Forensic Auditing in Healthcare.
  • Deloitte. (2024). Internal Investigation Trends in the Health Sector.

Copyright © 2025 American Institute of Healthcare Compliance All Rights Reserved

Read More
Auditing, Managing Denials Is Important to Good A/R Hygiene
Auditing

Fraud Indicators and Red Flags, Part 3

Part 3: When Unscrupulous Managers Turn Auditors Against Their Coworkers or Teams   

Written by Carl J Byron, CCS, CHA, CIFHA, CMDP, CPC, CRAS, ICDCTCM/PCS, OHCC and CPT/03 USAR FA (Ret)


We Recommend Reading Part 1:  When Audit Managers Knowingly Skew Audit Results and Part 2: When Criminal Behavior Infiltrates Your Audit Program. This final article in the Fraud Indicators & Red Flags series addresses potential outcomes when lead audit managers sabotage the audit process due to being insecure or due to the need to secure power in their position.

Introduction

In the first two articles over mid-level fraud indicators, we covered signs and solutions to the problem individuals. In this article we cover signs and methods to address auditors who have been “turned” into internal threats or “moles”; informing on their coworkers and/or teammates.

When unscrupulous managers or audit leads act alone or in a conspiracy to maintain their position, they will employ many short-term tactics. Because they have to constantly defend their activities, they will not think in terms of strategies except in some form of escape plan (covered in part 2). Managers or lead auditors who target subordinates to become informants stands alone, both in severity and damage to good employees and ultimately the organization: mid-level leaders targeting individual subordinates they have found to be malleable, weak, or easily intimidated/worn down. This is especially damaging to teams as cohesiveness and trust are critical to their work.

How Employees Are Turned

Retaliation

According to the U.S. Equal Employment Opportunity Commission (EEOC), “The most frequently alleged bases of discrimination were retaliation (39.2%), sex (35%), disability (34.3%), and race (16.8%). At the end of FY 2023, the EEOC had 227 merits cases on its active district court docket, of which 95 (41.8%) were class or systemic cases. Mar 27, 2024”. In the realm of equal opportunity, we tend to think of discrimination in its most well-known forms: employment discrimination because of your race, color, religion, sex (including pregnancy, transgender status, and sexual orientation), national origin, disability, age (age 40 or older), or genetic information. However, many cases have been litigated where an employee was retaliated against by a superior for voicing concerns, ethical complaints and maltreatment because of their job functions. To "discriminate" against someone means to treat that individual differently, or less favorably, for some reason.

While close timing between the allegation of retaliation and the manger's action can display retaliatory motive, there have been cases in which years have passed and other evidence established that the employee's prior activities set off the manager's action. Even minus close proximity timing, other relevant facts may include verbal or written statements; comparative evidence that a similarly situated employee was treated differently; falsity of the employer's ostensible reason for the adverse action or uncovered plausible deniability; or any other evidence from which an inference of retaliatory intent could be assessed. From the EEOC’s perspective, retaliation can take numerous forms: reprimand the employee or give a performance evaluation that is lower than it should be; engage in verbal or physical abuse; increase scrutiny; make the person's work more difficult; to name a few.

Managers find ways to retaliate against subordinates for bringing forward worries about fraud or questionable conduct. Rather than listening to the employee, who is normally an expert, many employers instead resort to various forms of blaming the messenger, and good employees are often fired, moved, or blackballed/driven from the healthcare arena for their willingness to speak up.

As in the parts 1 and 2, information is limited how mid-level administrators target individuals: but there are a number of recurring behaviors and types of bad actors who seek to isolate and “turn” auditors against their coworkers and teams.

Decentralization and Isolation

These arise from the same flaw(s) in any system but are used differently by the fraudster in a leadership capacity. The managers in question exploit the trust and lack of supervision of their activities: what controls may exist can be overridden (technology) or deflected (manipulating reports, meeting statements, etc.). Information asymmetry is used to manipulate technological data and remove negative information from reports, information the auditor will never see. If or when inquiries arise plausible deniability is used and the lack of oversight fully exploited.

There are two environments managers or audit leads use to isolate subordinates they wish to control: the office setting and the remote workforce.

In the office, if an auditor voices concerns or acts in a manner the manager sees as threatening or the manager has found to be easily influenced the manager may move the auditor away from coworkers or teammates or vice versa; move the team to other offices. The auditor now has no one they trust or can communicate with easily, directly and, critically, confidentially. Movements are harshly scrutinized and timeframes are strictly set to further control movement and communications. This isolation can be further abused by either the manager promising to put the team back together if the auditor “behaves”: or, the auditor is now so isolated maltreatment can be carried out at the manager’s will and the auditor turned to report what the manager wishes to hear when the audit team meets and works. Either way the team has been effectively infiltrated.

In the remote environment the manager already exploits information asymmetry but now, since the audit team cannot see each other at any point (in my experience Zoom and visual-virtual meetings do not fill the void of direct interaction), pressure can be put on individuals in turn and cracks either caused or taken advantage of. When conspiring managers work together and keep unrelenting pressure through implied or real threats (as viewed by the targeted auditor) and they force the auditors to only communicate with them individuals can feel lost and without options.

Bullying and Disrespectful Behavior:

Unfortunately, these behaviors have no direct legal protection: unscrupulous managers know this. They use both a combination of Game Theory and perverse incentives against individuals and together bullying and disrespectful behavior can wear an auditor down making them more malleable to turn against their team. Because of scarcity of information and similarities in definitions, bullying in this article is synonymous with disrespectful behavior, as they are virtually identical in practice.

An August 11, 2020 article in Forbes magazine titled The Differences Between Workplace Bullying And A “Hostile Work Environment” put the problem of protection against bullying as follows: “What then separates, on the one hand, a workplace that is miserable due to a boss who is a jerk to the entire staff and, on the other hand, a Title VII hostile work environment claim? The key is that the abusive conduct must be related to the employee’s race, sex, religion, etc. (otherwise known as a protected characteristic) in order for the mistreatment to be unlawful under Title VII and related laws. For example, if a manager has everyone walking on eggshells because they yell constantly and set unattainable goals/deadlines—but this abuse is directed to all employees—then this is not illegal under Title VII. If, however, the supervisor treated only female employees this way, then these women could pursue a hostile work environment claim if the inequity is based on their sex.”

For disrespectful behavior I direct the reader to a 2017 article published by The National Institute of Health: Disrespectful Behavior in Health Care-Its Impact, Why It Arises and Persists, And How to Address It—Part 2 by Matthew Grissinger: “Health care organizations have fed the problem of disrespectful behavior for years by ignoring it, thereby tacitly accepting such behaviors.  The health care culture has permitted a certain degree of disrespect while considering this a normal style of communication. Studies have shown that disrespectful behaviors are tolerated most often in unfavorable work environments, but it is unclear whether poor working conditions create an environment where the behaviors are tolerated or if the dis respectful behaviors create the unfavorable environment.

Organizations have largely failed to address disrespectful behavior for a variety of reasons. First, the behavior typically occurs daily but often goes unreported due to fear of retaliation and the stigma associated with “whistle blowing.” Disrespectful behaviors are difficult to measure, so without robust systems of environmental scanning to uncover the behavior, concerned leaders may be ignorant of the problem.  Leaders may also be unaware of the behavior if managers shield them from this information because they view it as a personal failure. If disrespectful behaviors are known, leaders may be reluctant to confront individuals if they are powerful or high-revenue producers, or they may not know how to handle the problem. It’s not a topic taught in training programs, so leaders may hesitate to take on a problem for which there is no obvious solution.”

The Workplace Bullying Institute (WBI), established in 1997 tackles the issues of prevention and protection against bullying. Since their institute began they have been “advocates for anti-workplace bullying legislation in the U.S. having introduced the Healthy Workplace Bill in California in 2003 and 31 other states and two territories since, WBI, in collaboration with David C. Yamada, Professor of Law, Suffolk University Law School, Boston, now brings forward an alternative model bill the Workplace Bullying Accountability Act (WBAA).”

The WBI has the most widely adopted definition of workplace bullying: “Workplace bullying is defined as an “abusive work environment” characterized by: repeated verbal abuse; conduct that is threatening, intimidating or humiliating; defamation of one’s reputation; work sabotage, undermining performance; and/or orchestrated ostracism.”

The WBI identifies multiple types of bullies:

  • The Constant Critic: “This one draws its targets behind closed doors. There they can threaten and intimidate without witnesses. Most shocking is that they target the most competent, veteran, go-to worker and claim that that target is incompetent. The stunning big lie freezes the target. If they are ever reported, they deny what they said and did. To HR, it becomes a she said/she said unsolvable problem. Their favorite tactic is to manufacture a false performance appraisal.”

We immediately see use of plausible deniability. If the manager is investigated they have a story ready-made, which can neither be proven nor disproven. No matter who gets involved the manager can always fall on “That’s not what I meant”; and so on. Because so much work is done remotely today this bully can plan and plot, and “test the waters” to find who the best targets are.

This bully will also take full advantage of information asymmetry. They make themselves, or them and a conspirator, the sole reporting avenues for all work, reports and performance evaluations. With decentralization and lack of robust controls documents will be manipulated, changed or deleted and the target sees no options. The bully may also have the ability to remove or corrupt auditor files. They cover two bases by verbally ordering the team to never report concerns or problems to each other or their supervisor: they strangle open communications. Their second layer of concealment is that the team will recognize the statement as an order and any attempt to circumvent or jump over them will result in accusations of insubordination. Since the manager controls upward information flow they can report what they choose, in what manner they choose. This creates and sustains an adversarial relationship between the manager(s) and the team and initiates the isolation stage of their scheme.

  • The Two-Headed Snake: “One moment your lunch buddy and a hugger. Right after, they stab you in the back. They are intent on controlling your reputation. To destroy it, they either start, or fail stop, rumors about you. This critter is very difficult to catch unless someone tells you what the snake has said about you.” This type includes the manager who either is friendly/polite, or says nothing: then months later you get a call from a superior informing you they were approached by the manager and a complaint lodged.

The two-headed snake also heavily exploits plausible deniability. This bully will do two things simultaneously: negatively/falsely report the auditor’s performance to their superior(s) and to the executives and omit reports and concerns voiced by the auditor completely: and be professional to the superiors they report to but harsh and untruthful to the auditor.

  • The Gatekeeper: “The Constant Critic and Two-Headed Snake do things to people. They commit acts of omission. Gatekeepers bully by withholding resources you need to succeed. Their dirty tricks are acts of omission. What do you need? Time to do the job? It’s denied by an impossible deadline. Information? You are blocked from using computers and search services. Furthermore, your colleagues have been ordered to not help you with anything. New job and you need training. No training for you. No budget. Though the department party is paid for. Need light duty coming back from surgery as the doctor ordered? No way. Management knows best and if you don’t return immediately to full duty, you will be fired.”

The auditor victimized by this type of bully actually may have immediate options to “return fire”. In parts 1 and 2 we covered fraud red flags and indicators of managers: and behaviors recognized by both the DoD IG and The State of New York Comptroller were withholding information. If the auditor feels there is no other starting point this can be immediately reported and investigated.

The WBI also has a position statement which encompasses, to a large extent, traits discussed in parts 1 and 2: “We believe a majority of bullies adopt the tactics of bluster and bravado as a cover, a mask, for some underlying deficiency. In other words, bullying is a compensatory set of behaviors meant to overcome something lacking — technical competence, empathy, or even fraud and theft.” This statement highlights another recognized red flag: Indications that key personnel are not competent in the performance of their assigned responsibilities.

If you as an auditor feel bullied, you are not alone. In an online survey conducted by the WBI some concerning numbers appeared:

  • falsely accused someone of “errors” not actually made (71%)
  • stared, glared, was nonverbally intimidating and was clearly showing hostility (68%)
  • discounted the person’s thoughts or feelings (“oh, that’s silly”) in meetings (64%)
  • used the “silent treatment” to “ice out” & separate from others (64%)
  • exhibited presumably uncontrollable mood swings in front of the group (61%)
  • made up own rules on the fly that even she/he did not follow (61%)
  • disregarded satisfactory or exemplary quality of completed work despite evidence (58%)
  • harshly and constantly criticized having a different ‘standard’ for the Target (57%)
  • started, or failed to stop, destructive rumors or gossip about the person (56%)
  • encouraged people to turn against the person being tormented (55%)

The last bullet point is exceptionally worrisome in the context of this article.

Being Selectively Unreachable:

When auditors are in the middle of their work, they often need rapid response from leadership to assist in problems, questions or the usual suspect, the “speed bump”. Especially in the remote environment managers will use these two ways: first they will be unreachable-period. And they will force the auditor to only approach them. Or they could call the auditor and demean them over the phone for their lack of knowledge knowing even if the behavior is reported likely no one will accept a phone call alone as evidence. But the manager will be faster than lightning to reprimand the same person. A chokehold has been put on communication but only to the individual. This causes tremendous stress and increases uncertainty because the auditor knows what awaits if he/she asks peers or an immediate supervisor for help and it gets discovered.

How to Spot the Informant

The auditor who bad actors have turned has several elements: was the auditor a good productive team member or was he/she already sarcastic, pessimistic or argumentive? On top of that, is the employee in an office setting or remote?

The Good Employee/The Unwilling Informant:

This is the majority of informants. In the office this may be visible early such as the example of the manager moving the team out or moving the auditor far away from the team. The remote environment is much more complicated for the team and much easier for the bad manager. The team does not see each other: as we have discussed communications have been forced to only the toxic manager so interactions between team members is tightly controlled: when an auditor has been targeted and pressure repeatedly put on the one auditor what communications take place do not allow the team to see potential effects. As discussed earlier even if the individual attempted to communicate directly with an immediate supervisor (but below the manager’s level) and the supervisor approached the manager, a plausibly deniable statement was ready.

The Not-so-Good or Easily Turned Employee:

There was already some real or perceived wrong by the individual and the manager’s insertion to further their “game” was not entirely unwelcome. In the office setting this might be dealt with by the meetings called by the bad actor(s): they want the team to feel their power and, not uncommonly, keep the team off balance and perhaps even maintain a certain amount of fear. The team will see the individual and either by statements made, favoritism shown by the bad actor toward the individual or other observed actions the team can as a collective element see a problem on the horizon. If the disgruntled auditor is separated from the team withholding information can go both ways and damage minimized. If the auditor remains with the team the team can collectively watch for signs such as excessive complaining and arguing, even over small points; complaining about being uninformed by the team; undermining team efforts to improve work, conditions or reporting functions; and disengagement from the team (good auditors can act this way as well: remember they do not want to be controlled and this may be an attempt to clue in the team).

With good and bad auditors, the remote environment complicates things-a LOT. Now the team does not know when the manager contacts the informant auditor, or about what. Meetings are remote and again the team cannot see each other (these managers do not use visual-virtual media for their meetings: it is another means to isolate individuals). The individual can even go so far as to start and maintain low level conflicts between her/himself and other members (as the bad managers do by initiating and maintaining disputes and adversarial relationships with the team).

An important behavior to look for is territorial behavior. Remember this individual was not unreceptive to the manager’s insertion into their work environment: they will do what they can to ensure no other team member discovers the alliance.

Other ways bad managers isolate good auditors have been discussed: but as they are more than likely indicators of fraud, they have more immediate avenues for elimination. They include Excessive control/micromanagement and forcing all control into the hands of 1-2 individuals; unclear expectations/vague “guidance” (withholding official or clear guidance they do not want known or applied).

Solutions

First and always at any sign of trouble even if only suspected document, document, document and wherever possible make bullet points tying complaints to a specific noncompliance, such as carrying on continuous disputes with the auditor and give official links to the guidances you used or attach them as Exhibits. Try to keep date-time groups as accurate as possible; and who said what when. Document what routes were attempted and what results were.

Most managers and lead auditors are ethical, hardworking and care deeply for their subordinates and the organization. The bad actors are the minority. When concerns arise about managers behaving fraudulently or antagonistically toward an auditor and their supervisor or the team another manager must be found who can address the situation and stay the course of reporting with an individual and/or the entire team. When the bad actors show themselves go to the good people and seek pathways to resolution. These people should be sought out by the team early and included in meetings if possible: or at the very least independently communicated with by a trusted teammate. This way communications are open, honest and in all likelihood big problems can be averted if the direct reporting mechanisms fail. A manager who is willing to isolate and turn an employee is not on the job for the right reasons: so, we can infer some form of fraud is taking place: financial, position protection or something else. It must be addressed quickly.

Even if a team member is believed/known to be an informant I still recommend sequestered team meetings. These are two-edged swords: the informant can report information the team shares which they rather the bad manager not be privy to: at the same time meetings can include “project assignments” or additional duties assigned to each member-the supervisor will likely be the lead for this. The supervisor can then contact each auditor individually with specifics added to their assignments. After a time, consistencies will appear because the manager(s) will micromanage everything and the informant will have shown her/his hand somewhere. In the office setting the team will need to look for more visible signs, as listed above.

The supervisor or first line leader can work directly with the informant. An unwilling participant in any fraudulent enterprise will likely want their position betrayed: they respect their team and want no part of whatever the manager is up to. Reporting safety nets and protections must be offered: confidentiality must be strictly adhered to: and the promise made of rapid action must at all costs be kept.

No solution has value unless there is a structure in place to proceed with it. Most big organizations have a hotline: whether via telephone or email the hotline must be reviewed regularly and every concern addressed. Unlike most systems if an auditor has been unwillingly turned against their team and the supervisor is assisting in the reporting process there should be an avenue for immediate supervisor/trusted individual input. Secondhand information may not be ideal but likely the auditor-informant (called a relator) is scared, stressed and afraid of retaliation, possibly including against their team. If first line leaders have enough tenure, they will likely know a peer in compliance or risk evaluation and rather than indirect communications, they can expedite the relator meeting directly with a party who has the authority to kickstart the resolution pathways. If possible, a direct internal line of reporting is advised. If the organization is big enough there may be an Ombudsman’s office to help pave the way.

Compliance and human resources cannot sit on their hands: but many departments either failed to believe the relator, initiate a serious investigation, or adhere to strictest confidentiality. Because these fraudsters know and game the system they will know as long as they refrain from certain behaviors and statements, civil rights type arguments will find little traction. The relators know this also: and if they are willing to come forward, they must have airtight guarantees of confidentiality-of the case they have reported and their identity and work environment.

Fraudster managers will “lock up” as many avenues of communication as they can internally and depending on their current tenure other sections, perhaps even compliance has been duped or kept so inaccurately informed they trust the manager(s) too much (again, information asymmetry and plausible deniability).

It is also recommended external avenues be established such as an attorney’s office, the contracting organization if the entity is a government contractor, or even an Arbitrator who can direct concerns efficiently and timely to the correct people. These are not recommended as first paths. However, if a relator has any doubt about their safety, then external measures should be established. Therefore, the team, again perhaps the Lead or supervisor should establish an external compliance “escape route”.

Now the deep dive: if any breach of process is suspected or prior attempts at resolution have failed. This is not recommended but may be necessary if the people reported to do not behave in a manner fitting the complaint. The relator has attempted internal controls and found them ineffective, even with as clear documentation and reporting as possible. This action comes with serious risk, there is no doubt: but resolution was honestly attempted and failed. Advise the addressees the relator is willing to take the case as high as necessary, even to the federal level.

My recommendation would be to word it as an advisory: “I have told you what I know, I expect proof of response within X# of days. If I hear nothing, or I receive any indications my confidentiality has been breached I reserve the right in accordance with (company, contractor) policy to report this to all authorities concerned with this matter. I am making a final attempt to resolve this problem locally and it is hoped at this point my concerns will be taken seriously. But if not, when reported to federal authorities the matter is out of our hands.” This statement will be taken seriously as intended: you have an argument and we need to address it, and you consider it very important. Or they could view it as a threat. Officially reporting the manager should be enough and the receiver(s) of the report should not need an advisory statement like this: you reserve this powerful addition to inform the receivers that you will see the matter through until a conclusion is reached and closed. So, it is up to the relator and any ally he/she may have to determine where in the process this goes-but have it ready. The relator has reported it at the lowest possible level: he or she must now commit to reaching as high as necessary to ensure all parties are dealt with and corrective changes made.

Conclusion

The vast majority of mid-level leaders are ethical and know their success relies on the true, realized accomplishment of the audit team below them. Attempting to turn a good or bad employee will never cross their minds because they hold themselves to a higher standard; and know deep inside that open communication delivered concurrently to all team members will achieve the highest rates of success.

Even where fraudulent managers exist these ethical managers will be as intolerant of their antics as the auditors. They will likely be an effective early avenue of reporting even if others who should be directly involved have failed.

Unfortunately, the damage mid-level fraudsters cause far exceeds the number working in the healthcare arena. Systems, processes and departments (i.e. Compliance) exist only to be disregarded and outmaneuvered: and individuals are expendable at any point so their illegal enterprise will survive. Elimination will only be achieved by teams and individuals willing to report them and defend their peers, and team cohesiveness strong enough to let each member know they are trusted and the team as a unit will support and if necessary, defend them.

About the Author

Carl J Byron, CCS, CHA, CIFHA, CMDP, CPC, CRAS, ICDCTCM/PCS, OHCC and CPT/03 USAR FA (Ret)

Carl is an experienced professional and contracted auditor with the military. His background includes HCC auditing for CMS, coding and auditing for a large global healthcare network, and serving as a compliance educator and speaker for AIHC. He currently volunteers as a subject matter expert for AIHC, a non-profit licensing and certification partner with CMS.

Copyright © 2025 American Institute of Healthcare Compliance All Rights Reserved

Read More
Auditing, Managing Denials Is Important to Good A/R Hygiene
Auditing

Fraud Indicators and Red Flags, Part 2

Part 2: When Criminal Behavior Infiltrates Your Audit Program 


Written by Carl J Byron, CCS, CHA, CIFHA, CMDP, CPC, CRAS, ICDCTCM/PCS, OHCC and CPT/03 USAR FA (Ret)   

We Recommend Reading Part 1 Fraud Indicators and Red Flags – When Audit Managers Knowingly Skew Audit Results as this article is Part 2, “the rest of the story.”

Subsequent to Part 1 - Fraud Indicators and Red Flags, this article stresses the need for early detection of that rare, but dangerous potential fraud committed by the Lead Auditor or Audit Manager.  Members of the audit team realize that detecting a non-conformance often means there is likely much that has gone undetected. If you see something, say something, right?  But what if it is your boss managing the audit?

Introduction

In this article, the term Audit Manager and Lead Auditor is used interchangeably, even though there may be variances between these two titles.  Audits are conducted as part of the organization’s compliance program for the purpose of detecting non-conformances in order to take corrective action to improve compliance to applicable rules and regulations. 

The assumption is made that most organizations have internal controls, checks and balances and accountability built into their compliance program.  When those controls fail, the audit process can be jeopardized, skewing audit results with a potential devastating impact on the risk management process.

Organizations, regardless of size, should require the following elements within an audit: Plan, Execute, Report, Corrective action (P-E-R-C).  Smaller healthcare organizations may only have one internal auditor, while mid-size and larger organizations have a team of auditors. Someone needs to manage or lead the audit, even if it is a team of only one auditor.  If your organization doesn’t engage with an independent third-party contractor to periodically inspect the management of the audit team, you should.  Typically, your Lead Auditor is the most skillful within our organization.  For an effective program, engaging an unbiased audit expert to review and “audit” the management of how audits are conducted is a sound risk management decision. 

Let’s review why auditing your audit program is so important.

Below the Surface: Detecting What You Don’t See

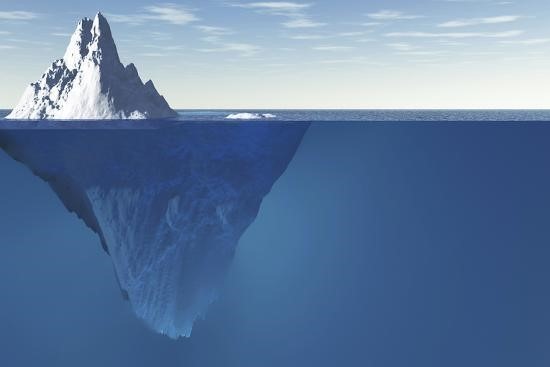
If your organization detects a problem, it is likely just the tip of the iceberg.  What you don’t or can’t see is likely to be a much bigger risk factor that what you do see. 

The assumption is made that most organizations have internal controls, checks and balances and accountability built into their compliance program.  Hopefully, this article describes several ways to detect areas of potential fraud within your audit processes.

It is not uncommon for C-suite Executives to delegate the responsibility of establishing and maintaining an effective internal compliance control system to mid-level management, such as the Lead Auditor, who must implement such controls at a reasonable cost. This could conflict with the Lead Auditor’s goals of improving coding, documentation, billing accuracy and other business systems.

It is the Lead Auditor’s primary responsibility to provide assurance that reviews are conducted to detect compliance non-conformance and to lead the audit team through the P-E-R-C proves.  For an audit program to be effective, audits must be conducted and reported in a manner free from material bias, conflict of interest and performed in an objective manner.  We must admit, auditing is not guaranteed to catch every instance of fraud, waste and/or abuse.  If a problem goes undetected, does this reflect poorly on the audit team?  It could, and it could result in tarnishing the team’s reputation.

But what happens when audit results are consistently exceptional?  Repeated scores of, let’s say 96%, 97%, 98% accuracy where the target performance goal is at least 95% accuracy?  Are these results “real” or should they be questioned?  Can Auditor Managers and Lead Auditors sway audit results to improve their own performance? Is it possible that the compliance infrastructure is unintentionally designed to encourage willful misrepresentation resulting in false positive outcomes?

These are important questions to ask to ensure the appropriate checks and balances are in place.  In-other-words, who is auditing the Lead Auditor? 

When Information is Withheld or Altered

Most organizations have effective audit programs led by experienced certified healthcare auditors.  Audit Managers and Lead Auditors are skilled at giving leaders independent, objective assurance that something is true. And auditors are experts when it comes to internal controls expected during an audit; unless that information is withheld or altered. Lead auditors, through training and experience, should be able to detect fraud indicators and when these indicators involve claims, then financial fraud may also be considered triggering an internal investigation. But having this much power, can it open opportunity for willful misrepresentation?

Let’s look at the government auditing standards for a moment.  In the 2018 Revision of Government Auditing Standards, the US Government Accountability Office it states (page 175, Section 8.73): “Fraud involves obtaining something of value through willful misrepresentation. Whether an act is, in fact, fraud is determined through the judicial or other adjudicative system and is beyond auditors’ professional responsibility.” 

Section 8.74 states: “Auditors may obtain information through discussion with officials of the audited entity or through other means to determine the susceptibility of a program to fraud, the extent to which the audited entity has implemented leading practices to manage fraud risks, the status of internal controls the audited entity has established to prevent and detect fraud, or the risk that officials of the audited entity could override internal control. An attitude of professional skepticism in assessing the risk of fraud assists auditors in assessing which factors or risks could significantly affect the audit objectives.”

Is Manipulating the Audit Environment a Sign of Malicious Activity?

Manipulating any part of the audit process requires investigation. This can involve acts of self-preservation on the Lead Auditor’s part, perhaps to the extent they want to drive out the more experienced auditors on the team who can uncover and report true findings and irregularities.

It is likely that experienced auditors on the team they manage may observe and question “why” something has navigated away from protocol. A red flag is when the Audit Manager’s motivations are questioned, the question is deflected or goes unanswered.

In my experience, opportunities exploited and behavior often found in those who are committing fraud, waste or abuse are those listed below, in addition to the typical collusion and conspiracy which are better known:

Weak Internal Controls – The manager is not monitored

The manager knows if concerns are voiced, the controls are so weak that little will come of complaint(s)-the manager also already has a script in place based on plausible deniability. Hyper-compartmentalization is exploited: departments are territorial and do not share information, i.e. Compliance does not oversee or meet with the auditing department. This causes a black hole between critical control components. There is no guarantee of confidentiality or protection. This too is exploited.

Moral hazard

A moral hazard occurs when one party in a transaction has the opportunity to assume additional risks that negatively affect the other party. The decision is based not on what is considered right but on what provides the highest level of benefit, hence the reference to morality.  In my experience, one of the more common is the moral hazard of rationalization.

Rationalizations are the excuses people give themselves for failing to live up to their own ethical standards. "Moral hazard of rationalization" refers to the psychological phenomenon where individuals use reasoning and justifications to convince themselves that their unethical behavior is acceptable, essentially allowing them to engage in immoral actions while maintaining a positive self-image, thus creating a "moral hazard" by reducing the perceived negative consequences of their actions; it's essentially using logic to excuse morally questionable behavior.1

Thorough knowledge of the systems and/or programs/Information Asymmetry

This is a serious element because the fraudster will have superior knowledge and/or access to electronic programs and processes.  When the Lead Auditor or Audit Manager has unlimited power through technology to manipulate data, routine monitoring is recommended of how this power is employed.  This is all part of strengthening internal controls through an objective expert.

The Payoff Matrix

According to an article in the National Library of Medicine published September 2023, in the context of healthcare fraud: "The Payoff Matrix refers to a conceptual framework that analyzes the potential outcomes (rewards and penalties) for different actors involved in fraudulent activities within the healthcare system, considering the choices they make between committing fraud or acting honestly, essentially illustrating the potential gains or losses depending on their decision and the actions of other parties involved, like patients, providers, and insurers; it helps visualize the incentives and disincentives that could influence their behavior towards fraudulent practices.”2

This is difficult for the vast number of honest managers to understand because they care deeply for their processes, employers, and, most importantly, people. To the fraudster it is a game; there are winners, there are losers; there are moves and counter-moves. They see the auditors as expendable players rather than victims: and they see superiors and leaders as opposing players who will be beaten and outmaneuvered. In the context of this article, they secure their positions and remain champions of the game, to continue with little thought to their own possible loss.

Detect the Tip of the Iceberg?

Actions to Mitigate Risk

The compliance department must be active, in place and independent in authority and action. If the reader will indulge a few analogies, I will show how critical this section of any organization is. About the iceberg analogy used in this article – the Titanic, the mighty, “unsinkable” ship, cutting edge in every way in its time.  We know on April 14, 1912 the Titanic hit an iceberg and sank igniting one of the most remembered tragedies in history.

Experts disagree on why the ship struck the iceberg but there are recurring theories: poor watch crew alertness and/or training; no binoculars; and they just didn’t see it in time. Things they do agree on: the ship was sailing too fast in known iceberg waters and there were not enough lifeboats.

Your compliance department is like the watch crew - They must look for hazards (watch): search for hazards in the future (binoculars): and have the authority to order the captain to alter course no matter how inconvenient. A compliance department that has become complacent or does not monitor internal controls is ignoring speed: things in healthcare move quickly. Having an ineffective compliance department is like having these lookouts not just make the ship hit the iceberg; they back the ship up and make it hit the iceberg again. Compliance must also be the lifeboats. They need to listen to and address every concern raised and treat all parties equally-no one stands alone because of title or position and the corollary; no one is above scrutiny for the same reasons. And compliance must be trusted to maintain strictest confidentiality. Every individual who reports concerns must feel they will be protected and safe.

The rest of the iceberg

In this image, note the long flat tabletop just below the surface. Managers who commit fraud, especially for their benefit at the cost of everyone else’s, will form some sort of escape route.

They are willing to “take some heat” as long as their fraudulent enterprise survives. The compliance department has to destroy this STAT. If the managers are spoken to but nothing substantial really is done, then they have taken the ship, backed it up, repaired it (so they think) and sent the ship right back into the iceberg.

Invest in Infrastructure & Developing a Culture of Compliance

Your workforce must feel “safe” to report concerns and observations of potential fraud, waste and/or abuse.  This only happens when a top-down culture of compliance has been instilled within the organization and demonstrated by the items listed below.

Responding to complaints must be rapid and effective - Compliance must be several critical things, just like the military: it must be forward yet visible (Air Force). We know they are active and they are watching beyond their office desks. We see them. They also must be agile: able to respond to indications or complaints quickly.  Employees at every level must know these people are there, always gathering information even when unseen and are there to defend them if necessary.

Compliance must also be the Army and Marines - Employees (relators) must know how to report concerns to the compliance department in a safe manner and undetected by the Lead Auditor when the Lead Auditor is of concern. Confidentiality must be the operative philosophy. Like all the major services, they must be able to act independently with the backing of the highest levels of authority. Above all, compliance must dedicate itself to an overarching creed: never let the relator feel scared, threatened, harassed or intimidated. Any form of retaliation will not be tolerated.

Establish a Confidential Network - The Audit Team needs to find an avenue to escalate complaints, confidentially, to those tasked with compliance and especially whistleblower protections. This should be between each auditor and the compliance officer or someone within the Compliance Committee. There really is power in numbers and just like plausible deniability, there will be force in consistency of fact. Because the auditors are external to the auditees, and in the remote environment external to the Audit Managers, information and concerns can be shared and options discussed without fear of harassment, reprisal or retaliation. Facts can be shared and supported by other auditors’ experiences.

This element differs from strengthening internal controls in that the point of contact for concerns need not absolutely be someone tasked with receiving them by policy.

Strengthen Internal Controls - There is no cookie-cutter template for succeeding in this. Whether through complacency, old school ways of thinking or the bureaucracy-wide need for self-preservation and avoidance of “bad news,” weak internal controls have devolved into weakness for a reason. Following right on the heels of getting these people to listen may be getting the auditors to trust them. Our attempts at reporting have failed: why should we trust you now? This is a legitimate question which must be answered before real progress can be made.

Documentation – Over time facts and details can become unclear.  Documenting observations, gathering “evidence” and making record in a timely manner can help determine if the person altering data has made a material falsification requiring a more formal internal (or external) investigation.

Conclusion

The vast majority of healthcare managers are ethical, hard-working people who care about their organization both downward and upward. They are as outraged by fraud or someone on their team manipulating information.  In my experience, the majority of published reporting of mid-level fraud regards financial motivation. If any healthcare organization takes firm and consistent steps to maintain strong internal controls, the type of fraud in this article will never see light and be mitigated before any significant damage can be realized.

Although we have covered quite a number of subjects, the solution will be driven by the establishment of a superstructure founded on ferreting out truth from plausible deniability and weak internal controls. Without these other efforts will yield little.

About the Author

Carl J Byron, CCS, CHA, CIFHA, CMDP, CPC, CRAS, ICDCTCM/PCS, OHCC and CPT/03 USAR FA (Ret)

Carl is an experienced professional and contracted auditor with the military. His background includes HCC auditing for CMS, coding and auditing for a large global healthcare network, and serving as a compliance educator and speaker for AIHC. He currently volunteers as a subject matter expert for AIHC, a non-profit licensing and certification partner with CMS. 
References

  1. McCombs School of Business – Ethics Unwrapped https://ethicsunwrapped.utexas.edu/glossary/rationalizations
  2. National Library of Medicine – Study on the Path of Governance in Health Insurance Fraud Considering Moral Hazard https://pmc.ncbi.nlm.nih.gov/articles/PMC10543491/#:~:text=Combating%20health%20insurance%20fraud%20is,toward%20a%20non%2Dfraudulent%20state

Copyright © 2025 American Institute of Healthcare Compliance All Rights Reserved

Read More
Auditing, Managing Denials Is Important to Good A/R Hygiene
Auditing

Compliance & Internal Investigations

Written by: Joanne Byron, BS, LPN, CCA, CHA, CHCO, CHBS, CHCM, CIFHA, CMDP, COCAS, CORCM, OHCC, ICDCT-CM/PCS


Are you an internal auditor conducting “routine” reviews? Have you ever uncovered erroneous or potentially fraudulent evidence? Once your suspicions have been reported to the Compliance Officer, were you asked to partake in evidence gathering during the investigation? The content of this article is for educational purposes and not intended as consulting or legal advice.


For those of you more experienced auditors, additional training in how to handle evidence during an internal investigation not only advances your career but helps secure evidence that can be used if an actual crime has been committed. I also recommend reading When Healthcare White-Collar Crimes Turn Red, an AIHC blog article from 2021.


Do you need to convince executives that crime is a potential problem for your organization? The Department of Justice (DOJ) posts “News & Noteworthy” cases here. 


What Comes to Mind When You Hear the Word “Forensic”?


Most of us think about investigations as seen on television programs, such as “CSI” or “Bones.” Forensic science is a critical element of the criminal justice system – “Forensic scientists examine and analyze evidence from crime scenes and elsewhere to develop objective findings that can assist in the investigation and prosecution of perpetrators of crime or absolve an innocent person from suspicion.”


According to the Merriam-Webster dictionary, the word forensic is defined as the following:

  • Belonging to, used in, or suitable to courts of judicature or to public discussion and debate
  • Relating to or dealing with the application of scientific knowledge to legal problems

Your auditing and compliance skills become valuable to professional law enforcement, but you need to know what, when and how to handle a situation which could potentially turn into criminal charges against someone within your organization. First, let’s start with prevention.


Is It an Internal or External Investigation?


Internal Investigations are conducted by skilled employees (or a consultant under contract working for the organization) trained to perform specialized audits to gather evidence when there is suspected fraud, abuse or crime. These investigations are typically conducted to gather information sufficient for legal counsel to determine whether an external investigation is warranted by the appropriate authorities.  These employees are often referred to as Internal Forensic Auditors or Internal Investigators. For the purpose of this course, we will refer to this position as an Internal Forensic Auditor.


Internal Forensic Auditors report to a Board of Directors, Compliance Officer and/or Audit Committee of the health care organization and typically work under the direction of the organization’s legal counsel.


External Forensic Auditors are independent of the organization they are auditing. They are experts working as an investigator for an accounting or consulting firm, CMS, a police department, the FBI or another agency as described above.


The process of conducting a forensic investigation is, in many ways, similar to the process of conducting an audit, but with some additional considerations. The various stages are briefly described below. 


Step 1: Accepting the Investigation


Review information regarding the matter and consider whether you (and your team) have the necessary skills and experience to accept the work.

  • Forensic investigations are specialized in nature, and the work requires detailed knowledge of fraud investigation techniques and the legal framework.
  • Investigators must also have received training in interview and interrogation techniques and in how to maintain the safe custody of evidence gathered.
  • Investigators must be able to address potential conflicts of interest or bias and achieve objectivity.

Step 2: Planning the Investigation


The investigating team must carefully consider what they have been asked to achieve and plan their work accordingly. The objectives of the investigation will include:

  • Recognize if there is sufficient evidence to warrant a forensic investigation. If so, then anticipate planning required to achieve the following:

      o Identify the type of fraud that has been operating, how long it has been operating for,
    and how the fraud has been concealed;

           Determine deadlines and timeframes to complete the investigation which may
    be driven by regulatory factors;

      o Identify the fraudster(s) involved;

      o Quantify the financial loss suffered by the organization;

      o Gather evidence for potential use in court proceedings;

           Identify the type of report format required and record evidence appropriately; and

      o Provide advice to prevent the reoccurrence of the fraud. 

The investigators should also consider the best way to gather evidence. They may choose the use of computer assisted audit techniques or other various methods appropriate for the situation.


Step 3:  Gathering Evidence – Fact Finding


In order to gather detailed evidence, the investigator must understand the specific type of fraud that is suspected. The evidence should be sufficient to ultimately prove the identity of the fraudster(s), the mechanics of the fraud scheme, and the amount of damage or loss suffered by the organization.


It is important that the investigating team is skilled in collecting evidence that can be used in a court case and in keeping a clear and secure chain of custody until the evidence is presented in court. If any evidence is inconclusive, or there are gaps in the chain of custody, then the evidence may be challenged in court or even become inadmissible. Investigators must be alert to documents being falsified, damaged or destroyed by the suspect(s). 


“Chain of custody” is defined by Dictionary.com as “the order in which a piece of criminal evidence should be handled by persons investigating a case, specifically, the unbroken trail of accountability that ensures the physical security of samples, data and records in a criminal investigation.” To prove the chain of custody, and ultimately show that the evidence has remained intact, prosecutors generally need internal investigators who can testify:

  • That the evidence offered in court is the same evidence they collected or received.
  • To the time and date the evidence was received or transferred to another provider.
  • That there was no tampering with the item while it was in custody.

Evidence can be gathered using various techniques, including: 

  • Testing controls to gather evidence which identifies the weaknesses which allowed the fraud to be perpetrated;
  • Using analytical procedures to compare trends over time or to provide comparatives between different segments of the business;
  • Applying computer assisted audit techniques which may help to identify the timing and location of relevant details being altered in the computer system;
  • Discussions and interviews with employees;
  • Substantive techniques such as: reconciliations, cash counts and reviews of documentation.

Step 4: Analyzing Data


After evidence and facts have been gathered and recorded, it is time to analyze all the data. The goal of data analysis is to determine if there is a relationship between the independent and dependent variables and to look for patterns within the data. 


Recording and organizing data may take different forms depending on the kind of information being collected. The way you collect your data should relate to how you’re planning to analyze and use it. Regardless of what method you decide to use, recording should be done concurrently with data collection if possible, or soon afterwards, so that nothing gets lost and memory doesn’t fade. Some of the things to do with the information collected can include:

  • Gather together information from all sources and observations;
  • Make photocopies of all recording forms, records, audio or video recordings, and any other collected materials to guard against loss, accidental erasure, or other problems;
  • Enter narratives, numbers, and other information into a computer program where they can be arranged and/or worked on in various ways;
  • Perform any mathematical or similar operations needed to get quantitative information ready for analysis;
      o These could include entering numerical observations into a chart, table, or spreadsheet, or figuring the mean (average), median (midpoint), and/or mode (most frequently occurring) of a set of numbers.
  • Transcribe (making an exact, word-for-word text version of) the contents of audio or video
    recordings;
  • Code data (translating data), particularly qualitative data that isn’t expressed in numbers, into a form that allows it to be processed by a specific software program or subjected to statistical analysis; and
  • Organize data in ways that make it easier to work with. This will depend on your research design and your evaluation questions.
      o Consider grouping observations by the dependent variable (indicator of success) they
    relate to, by individuals or groups of participants, by time, by activity, etc.
      o You might also want to group observations in several different ways so that you can study interactions among different variables. 

There are two kinds of data you’re apt to be working with. However, not all evaluations will necessarily include both.

  • Quantitative data refers to the information that is collected as, or can be translated into, numbers which can then be displayed and analyzed mathematically.
  • Qualitative data can be collected as descriptions, anecdotes, opinions, quotes, interpretations, etc. They are generally not able to be reduced to numbers and/or are considered more valuable or informative if left as narratives.

As you might expect, quantitative and qualitative information need to be analyzed differently. The investigation is likely to lead to legal proceedings against one or several suspects. Therefore, members of the investigative team must be comfortable with appearing in court to explain how the investigation was conducted and how the evidence was gathered.


Step 5: Report Your Findings


Draft the report in an objective manner. Do not draw conclusions, just report the facts. The checklist below summarizes what a typical report should contain:

  • Provide a Summary of the Investigation or Case
  • Describe the Investigation Plan
  • Case Notes – Keep an Investigator Diary
  • Information Interview Summaries
  • Interview Reports
  • Analysis of Investigation
  • Conclusion
  • Recommendations and Additional Action(s) Required With This Case
  • Exhibit Listing - attachments and evidence related to the case

Conclusion


An Ounce of Prevention Is Worth a Pound of Cure – So Learn More About Health Care Crime


A little precaution before a crisis occurs is preferable to a lot of legal complications, “bad press” and huge potential losses afterward. Preventing fraud in your organization starts with not hiring criminals! That might sound ridiculous, but are we really doing everything we should during the hiring phase of employees and contractors?


Most organizations are using the LEIE on the OIG website to screen new hires and conduct monthly verifications. But is this enough?


Unverified employees can put your organization at risk with a dramatic impact on your company’s brand reputation, performance and finances. Screening employees at hire, and periodically during employment, is a must for creating a safe workplace.


Below is a “short list” of screening tactics to consider before extending an offer to a candidate for hire. Be sure to review your procedure with legal counsel or a human resources expert to avoid any potential legal consequences with the U.S. Equal Employment Opportunity Commission (EEOC) related to changing your current hiring practices.

  • Criminal background check
  • Office of Inspector General (OIG) Exclusions Database check
  • Education – verify graduation, degree
  • Professional Certifications (check all certifications with the certifying agency – do not accept certificates from the potential employee as proof)

The EEOC has a webpage dedicated to help employers that addresses “Background Checks – What Employers Need to Know.” The information on this page is a joint publication between the EEOC and the Federal Trade Commission or FTC.


When making personnel decisions, which include hiring, retention, promotion, and reassignment, the EEOC states that employers should consider the background of applicants and employees. For example, the EEOC states you may want to consider verifying:

Except for certain restrictions related to medical and genetic information (per HIPAA, addressed further on the EEOC website), it's not illegal for an employer to ask questions about an applicant's or employee's background or to require a background check.


AIHC offers training – a “how to” participate in or conduct an internal investigation. The course is offered online with the option to certify (with a professional proctor online). The program is entitled Internal Forensic Auditor. If this course seems too intense, you may want to begin with the Auditing for Compliance online program.

Read More